API keys, limits and CORS
Give partners and apps their own keys, set rate limits and allowed origins, and see usage and credits per day.
Updated October 25, 2026
A published API sits behind the Craftkite gateway. It checks the caller's key and scopes, applies limits and CORS, and only then passes the request to your API with a signed identity.
Consumers and keys
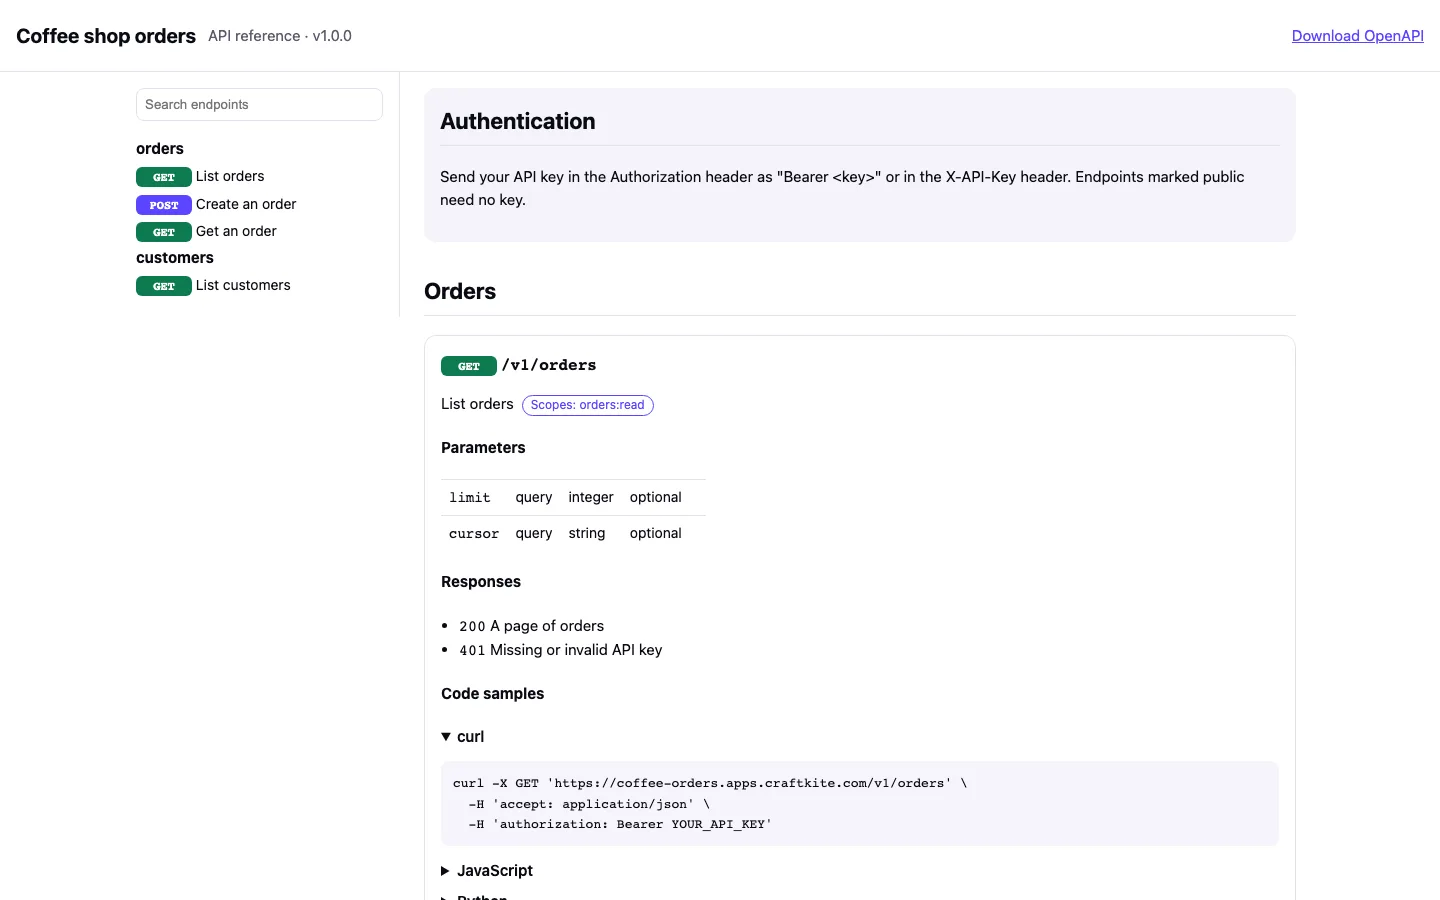
In the API tab open Consumers, add a consumer (a partner, an app, a customer) and set its requests per second and requests per day. Create a test key or a live key: it is shown once — copy it then; Craftkite keeps only a fingerprint. Callers send it as Authorization: Bearer ak_live_… or X-API-Key. Revoke stops a key at once.
CORS and the API reference
Under Settings, list the allowed origins of websites whose browsers may call the API; * cannot be combined with cookies. Choose whether the reference at /docs is open to everyone, only with a key, or off.
Usage, credits and new versions
Usage shows requests, server errors and response times per day and per consumer. Requests through the gateway cost one credit per the number of requests in the credit table, booked once a day. Before a publish, Craftkite compares the new version with the live one: changes that break existing consumers (a removed endpoint or field, a new required field) need your confirmation, and a /v2 path is suggested.